Overview
Wazuh is a free, open-source security platform that brings together SIEM (Security Information and Event Management) and XDR capabilities. It collects and analyses logs and endpoint data through agents, applies detection rules, performs file-integrity monitoring and vulnerability detection, and maps findings to frameworks such as MITRE ATT&CK.
| Attribute | Summary |
|---|---|
| Vendor | Wazuh |
| Category | Security Operations |
| Deployment | Self-hosted on-premises or cloud |
| Licensing | Open source (free); paid cloud and support available |
| Best for | A free, extensible SIEM/XDR platform you control |
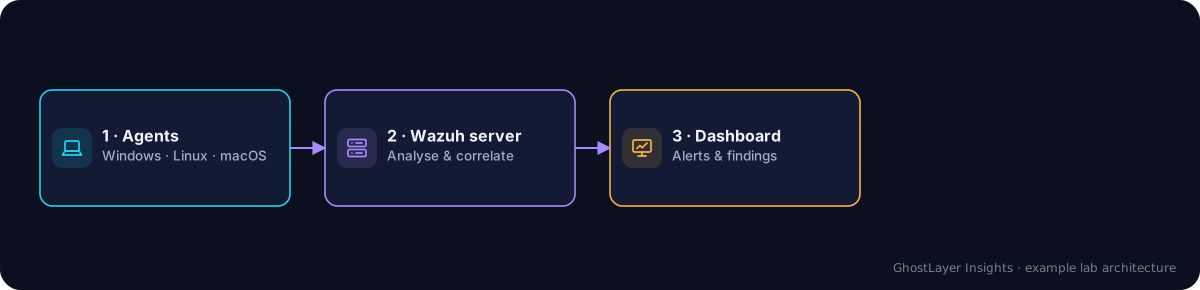
Select any component in the diagram to read what it does.
Text description of this diagram
Agents on hosts send data to the Wazuh server, which applies detection rules; the dashboard presents alerts and findings.
Key features
- Log data collection and correlation across many sources.
- Host-based intrusion detection, file-integrity monitoring (FIM) and rootkit checks.
- Vulnerability detection and configuration assessment.
- Detection rules mapped to MITRE ATT&CK, with a dashboard for analysts.
- Cross-platform agents for Windows, Linux and macOS.
Strengths
- Free and open source, with no per-endpoint licence cost.
- Highly flexible and extensible, with an active community.
- Broad coverage spanning SIEM, endpoint monitoring and compliance.
- Clear mapping of detections to MITRE ATT&CK aids investigation.
Limitations to weigh
- Self-hosting means you manage deployment, scaling and tuning yourself.
- Getting the most from it benefits from in-house security expertise.
- Support is community-based unless you buy a paid cloud or support plan.
Deployment options
Wazuh is typically self-hosted — as a single-node lab or a distributed, multi-node deployment for larger environments — and a managed cloud offering is also available from the project.
Integrations
- Threat-intelligence feeds and enrichment sources.
- Ticketing, chat and SOAR tools for alert workflows.
- A flexible rule and decoder system plus APIs for custom integration.
Licensing
The Wazuh platform is open source and free to use. Optional paid cloud hosting and commercial support are available from the project for teams that prefer a managed service or formal support.
Ideal use cases
- Teams building a cost-effective, in-house SIEM/XDR capability.
- Organisations needing file-integrity monitoring and compliance checks.
- Labs and learners exploring security monitoring hands-on.
New to this area? GhostLayer Insights has a dedicated SIEM with Wazuh course in the Learning Hub.
This is an independent editorial overview based on publicly available vendor documentation and general industry knowledge. It is a demonstration review: it is not a paid placement, a hands-on lab test, or a benchmark, and it does not assign a numeric rating. Always confirm current specifications, licensing and pricing with the vendor before making a decision.