Overview
CrowdStrike Falcon is a cloud-delivered endpoint protection platform that combines next-generation antivirus with endpoint detection and response (EDR) and extended detection and response (XDR). Its defining idea is a single lightweight agent that reports to the cloud, where detection, analytics and threat intelligence are processed.
| Attribute | Summary |
|---|---|
| Vendor | CrowdStrike |
| Category | Endpoint Security |
| Deployment | Cloud (SaaS), single agent |
| Licensing | Commercial subscription (per endpoint, modular) |
| Best for | Cloud-native EDR/XDR with managed threat hunting |
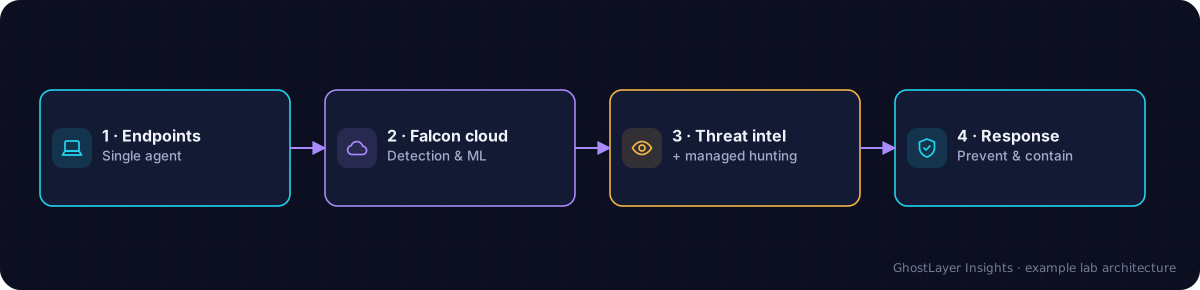
Select any component in the diagram to read what it does.
Text description of this diagram
A single lightweight agent on each endpoint reports to the cloud, where detection, analytics and threat intelligence run.
Key features
- A single lightweight agent covering prevention, detection and response.
- Behaviour-based detection and machine-learning analytics in the cloud.
- Integrated threat intelligence and optional managed threat hunting.
- Modular platform (prevention, EDR/XDR, device and identity visibility, and more).
- Broad OS support for Windows, macOS and Linux.
Strengths
- Lightweight agent with cloud-side processing reduces endpoint overhead.
- Strong, widely recognised detection and threat-intelligence capabilities.
- Cloud delivery scales well and simplifies deployment and updates.
- A broad module ecosystem lets organisations expand coverage over time.
Limitations to weigh
- Subscription and per-module pricing can add up for large estates.
- Full value depends on reliable cloud connectivity.
- The breadth of modules can make licensing choices complex.
Deployment options
Falcon is delivered as a cloud service; organisations deploy the single agent to endpoints and manage policy from the cloud console. There is no on-premises management server to maintain.
Integrations
- SIEM and SOAR platforms for alerting and automated response.
- Identity providers and IT service-management tools.
- An API and marketplace for extending the platform.
Licensing
Falcon is licensed as a commercial subscription, typically priced per endpoint with different tiers and add-on modules. Confirm current tiers, module bundles and pricing directly with the vendor.
Ideal use cases
- Enterprises standardising on cloud-native endpoint protection.
- Teams that want EDR/XDR with optional managed threat hunting.
- Organisations consolidating endpoint, identity and threat intelligence.
This is an independent editorial overview based on publicly available vendor documentation and general industry knowledge. It is a demonstration review: it is not a paid placement, a hands-on lab test, or a benchmark, and it does not assign a numeric rating. Always confirm current specifications, licensing and pricing with the vendor before making a decision.